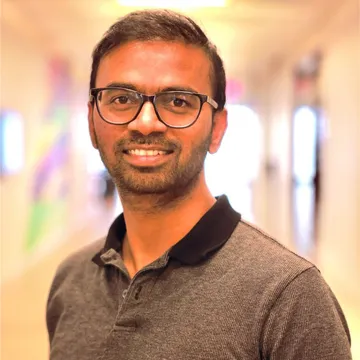
Forward Deployed Engineer · Principal, Comcast

I embed with engineering teams and ship the security tools they actually adopt.

Naresh Kyadarwar. Ten-plus years of software engineering, spent sitting inside the teams I build for — from enterprise Java and ecommerce microservices on AWS to the DevSecOps platforms I now ship at Comcast scale.

Fort Washington, PA

AWS Certified DeveloperAWS Certified AI Practitioner
Naresh Kyadarwar
Naresh KyadarwarForward Deployed Engineer · Fort Washington, PA
10+years in software engineering
2AWS certifications
3enterprise employers: Comcast, Tivity, Walgreens
MCAOsmania University

01About

I'm a Forward Deployed Engineer at Comcast, Principal level. Instead of building security tooling from a central platform team and handing it over, I embed directly with application teams, learn their real delivery problems, and build the DevSecOps products that improve their security posture alongside them: tools that help them find, prioritise and fix issues without slowing down.

My approach has three parts. Give leaders decisions, not data: turn security signals into exposure, common problems and next actions. Meet developers where they work: self-service remediation inside the an internal Backstage developer portal. Build reusable, not bespoke: templates, skills and data pipelines that every team can adopt.

I came to this from full-stack and backend engineering on high-traffic ecommerce and payments systems on AWS, which is why I design security tooling the way a developer wants to use it. More recently I built an AI agent orchestrator — with agents for security information, change management, server rotation, diagnostics and remediation guidance — that automates patching workflows on a cloud-native platform on Kubernetes.

// forward_deployed

  1. Embed with the teamWork alongside application teams to understand their real security and delivery problems, not a generic backlog.
  2. Build the product with themDesign and ship DevSecOps tooling that fits how they already build, test and deploy.
  3. Make it reusableTurn what works into self-service tools, templates and skills that other teams can adopt.

02Experience

  1. May 2020 – Present

    Principal Engineer Comcast

    • Work as a forward-deployed engineer: embed directly with application teams to build DevSecOps products that improve their security posture, from first problem to adopted tool.
    • Built an AI agent orchestrator and the agents around it — for security information, change management and server rotation, among others — on LangGraph, with an MCP server, an LLM gateway and Langfuse tracing, running on a cloud-native Kubernetes platform.
    • Built an IDE security plugin that runs secret scanning, Snyk scanning and SonarQube checks as git pre-commit hooks, calling an internal secret-scanning service over SSO to catch and stop secrets before they're ever committed.
    • Design and build cloud remediation tools in an internal Backstage developer portal: an AWS Key Rotation plugin that auto-remediates keys once they're due for rotation, IMDS Remediation, and S3 policy updates.
    • Built AI tools that help developers remediate Snyk findings faster against existing Snyk and Dependabot pull requests, plus auto-patching tools that remediate infrastructure vulnerabilities directly.
    • Built a leadership security-insights dashboard that tells engineering leaders their exposure, common problems and next actions, with a portfolio status view.
    • Build the ETL pipelines (Concourse, AWS Batch) that supply trusted data to these tools.

    Forward DeployedDevSecOpsAI AgentsLangGraphMCPKubernetesIDE PluginAI RemediationCloud RemediationBackstageDeveloper ExperienceConcourseAWS BatchETL

  2. Jul 2014 – Apr 2020

    Full Stack Web Developer Tivity Health (formerly Nutrisystem)

    • Built and ran catalog microservices on AWS EC2 for nutrisystem.com and southbeachdiet.com, fronted by API Gateway for authentication and monitoring.
    • Moved CI/CD from Bamboo to Jenkins, and built Java / Spring components for ratings, reviews and payments (Cybersource, PayPal, Google Pay, Apple Pay).

    JavaSpring BootAWSJenkins

  3. Aug 2013 – Jul 2014

    Senior Java Developer Walgreens

    • Designed RESTful services for catalog, cart and checkout in a responsive web redesign, and built Spring authentication services.
    • Root-caused production concurrency and transaction issues, and introduced JUnit testing to raise quality.

    JavaSpringRESTJUnit

03Selected work

// ai_agent_orchestrator

AI Agent Orchestrator

An orchestrator and five purpose-built agents that automate the patching workflow, on a cloud-native Kubernetes platform.

  • Security Info Agent: surfaces the security context each step of the workflow needs.
  • Change Management Agent: creates change tickets automatically.
  • Server Rotation Agent: rotates servers ahead of patching.
  • Plus agents for diagnostics and remediation guidance.

Built on LangGraph, with an MCP server exposing toolsets to the agents, an LLM gateway for model access across providers, and Langfuse for tracing.
AI AgentsLangGraphMCPLLM GatewayLangfuseKubernetesCloud NativeOrchestrationPatch Automation

// ide_security_plugin

Developer IDE Security Plugin

Stops secrets at commit time, before they ever leave a developer's machine.

  • Secret scanning, Snyk scanning and SonarQube checks, wired in as git pre-commit hooks inside the IDE.
  • SSO-based integration calls an internal secret-scanning service to detect secrets in real time.
  • Gives developers feedback and blocks the commit, instead of catching the secret after the fact.

IDE PluginSecret ScanningSnykSonarQubeGit HooksSSO

// leadership_insights

Leadership Security Insights Dashboard

Turns security data into decisions for engineering leaders.

  • Exposure: where a leader's teams are exposed right now.
  • Common problems: the recurring issues across their portfolio, so one fix can help many teams.
  • Next actions: a prioritised list for each team, not just a list of findings.
  • Portfolio status: a single view of how the whole portfolio is doing.

Application SecurityAnalyticsLeadership reporting

// backstage_remediation

Cloud remediation tools in an internal developer portal

Self-service fixes inside a Backstage app, where developers already work.

  • AWS Key Rotation plugin: auto-remediates access keys once they're due for rotation.
  • IMDS Remediation: fixing instance metadata service configuration on AWS compute.
  • S3 policy updates: correcting bucket policies.
  • Each one turns a security finding into a guided fix, in one place.

BackstageAWSCloud RemediationSelf-service

// ai_remediation

AI-assisted vulnerability remediation

Closing the gap between a finding and a fix.

  • AI tools that help developers remediate Snyk findings faster, working against existing Snyk and Dependabot pull requests.
  • Auto-patching tools that remediate infrastructure vulnerabilities directly, without waiting on a developer to pick up a ticket.

AISnykDependabotAuto-patchingVulnerability Remediation

// data_pipelines

ETL data pipelines

The data foundation behind the insights.

  • ETL jobs orchestrated in Concourse.
  • Heavy data processing on AWS Batch.
  • Reliable, repeatable data that the tools and dashboards depend on.

ConcourseAWS BatchETLAWS

04Skills

Languages & backend

JavaPythonSpring BootSpring Data JPARESTJavaScript

AWS cloud engineering

EC2IAMS3LambdaAWS BatchAPI GatewayDynamoDB

Platform & developer experience

BackstageConcourseJenkinsGitHubTemplatesInternal tooling

AI agents & cloud native

AI Agent OrchestrationLangGraphMCPLLM GatewayLangfuseMulti-agent SystemsKubernetesCloud Native

Security & remediation

Key rotationIMDSS3 policyIAMSnykSonarQubeSecret scanningGit hooksSSO

Data & observability

ETLAWS BatchOracleMySQLDynamoDBSumologic

Earlier toolkit

MavenAntJBossWebLogicOracle CommercejQuerySOAP / SoapUI

05Latest thoughts

All articles →
·4 min

AI agents for security remediation, and what they do for developer experience

Finding vulnerabilities is solved. Fixing them is the bottleneck. Where agents help, where they don't, and the guardrails that make them safe to run at scale.

ai-agentsappsecdeveloper-experience

·1 min

Hosting a static site on S3 with CloudFront

A practical checklist for serving a static site securely from a private S3 bucket behind CloudFront, with sensible caching.

awss3cloudfront

06Through the lens

Full gallery →
Yellow wildflowersGlacier above a mountain lakeGlacial stream in bloomGlacial stream in bloom alternate editSandstone coastlineCanyon under storm clouds

Let's build something useful and reliable.

nkyd.tech@gmail.com